
Your network has answers
to questions you haven't
asked yet.
Most manufacturers we talk to aren’t careless. They’re stretched. An acquisition closes, a new plant comes online, the IT team inherits infrastructure nobody fully mapped — and somewhere in that complexity, hides the unknown
We find it. In 3 days. With less than 30 minutes
of your team's time.
 Critical Operations Focused3,600+ Penetration Tests
Book Now & Get Started
Limited slots available. Pick a time, and we'll take it from there.
Your information stays private.
Your network has answers to questions you haven't asked yet.
Critical Operations
Focused
3,600+ Penetration
Tests
We find it. In 3 days. With less than 30 minutes of your team's time.


Why Choose Us
We don’t hand you a spreadsheet and wish you luck.
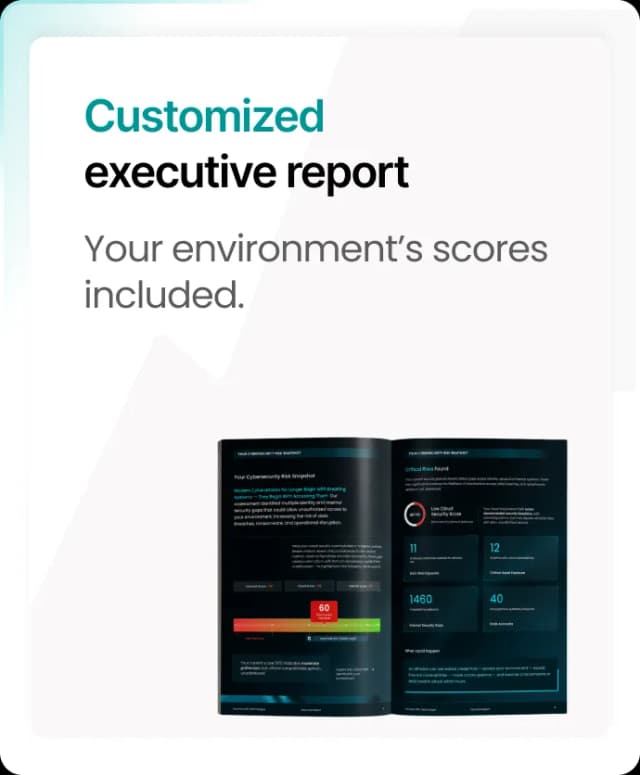
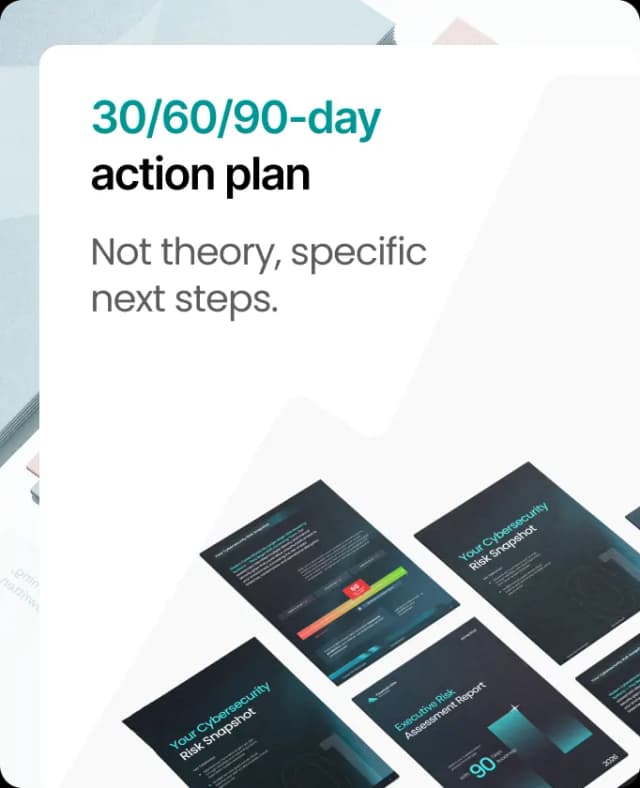
For every Security Jumpstart, we build a customized, 25+ pages executive security report tailored to your environment. Not numbers on a chart, but an actionable plan — one that your IT team can implement Monday morning, and your board can read without a translator.
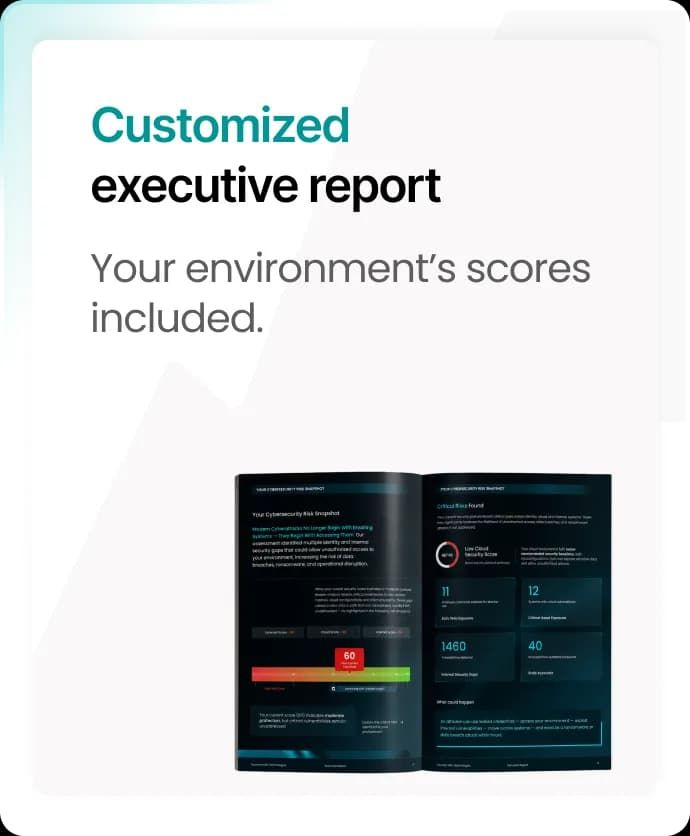
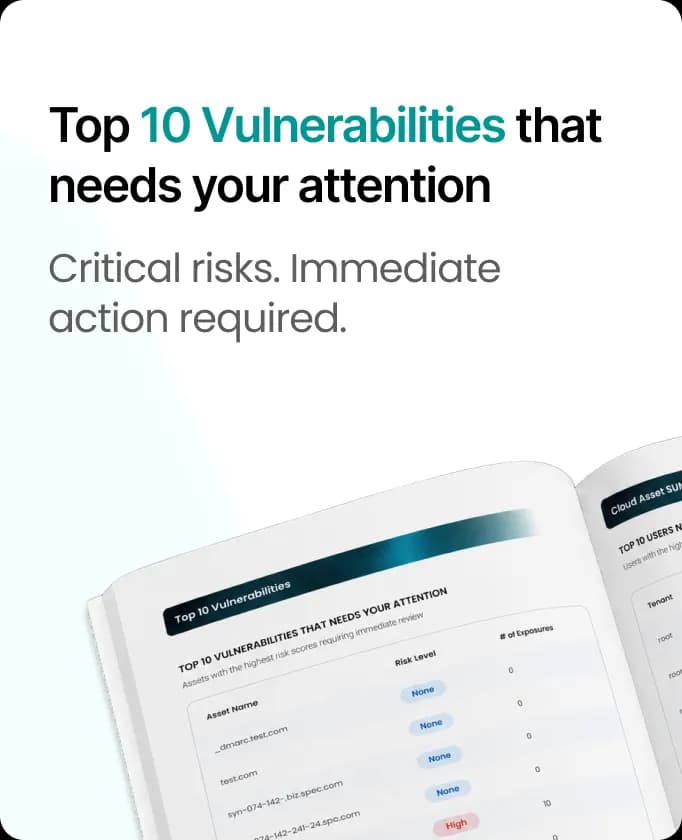
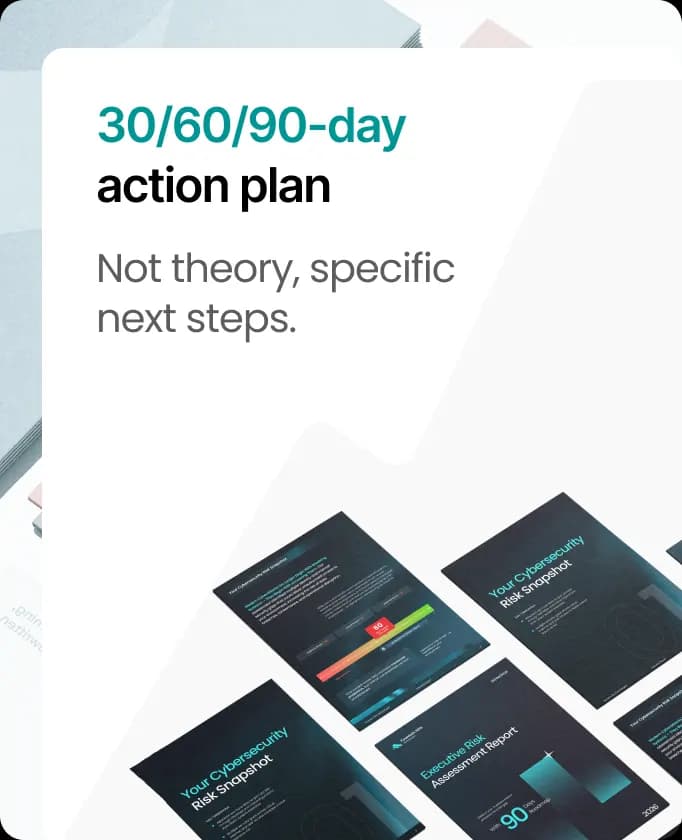
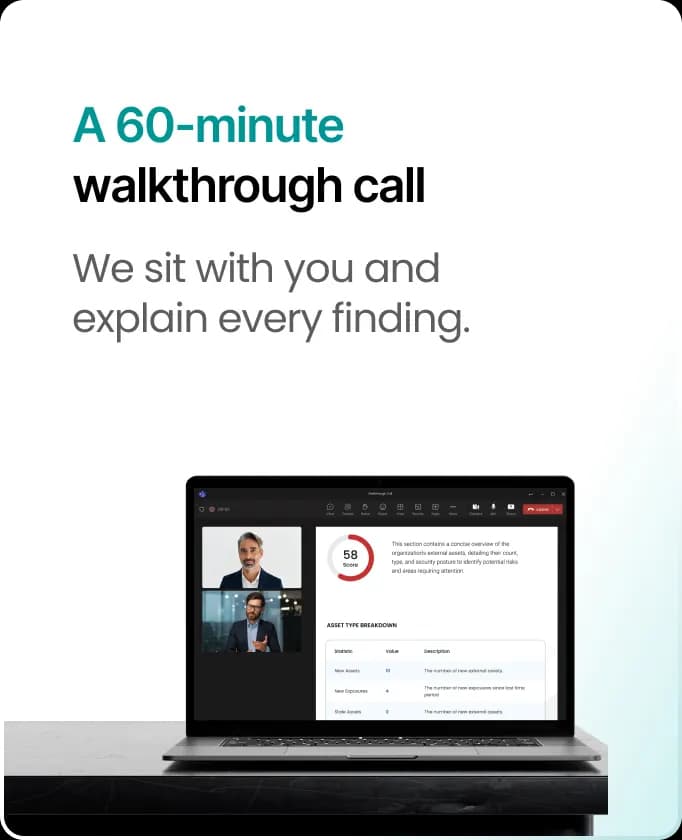
What We Analyze Across Your Business.
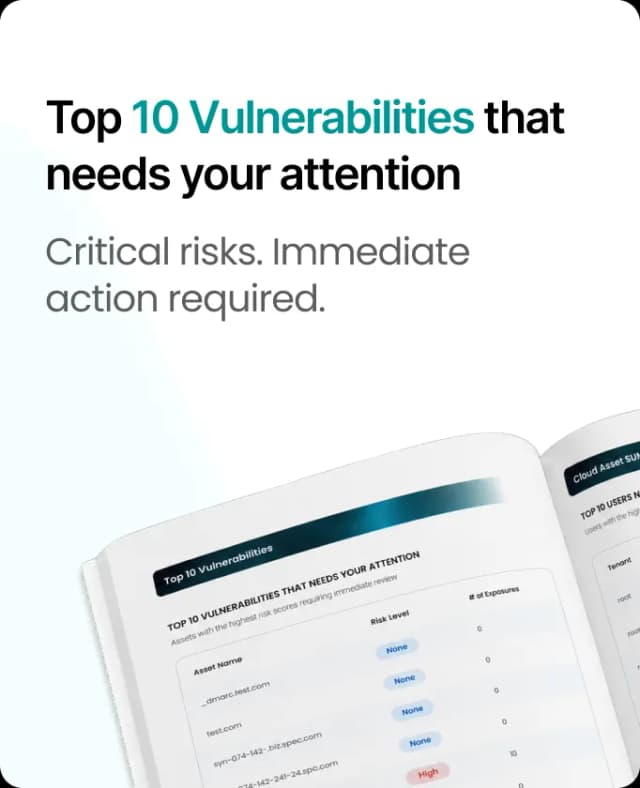
Most businesses only see part of their risk. We analyze every layer — external exposure, internal systems, cloud environments, and identity gaps — to uncover what's actually vulnerable before attackers do.

External Attack Surface
Your websites, subdomains, exposed IPs — everything an attacker sees before they ever touch your firewall. Most manufacturers don't know half of what's visible.

Internal Network
Servers, desktops, printers, IoT devices, switches — the stuff behind your firewall that nobody's looked at in a while. This is where the surprises live.

Cloud & Microsoft 365
User accounts, authentication gaps, M365 misconfigurations. We measure your setup against CISA baselines — and the gaps are almost always bigger than expected.

Dark Web Exposure
Uncover employees' credentials that may be circulating in breach databases. We scan and highlight old inactive employees accounts as well as current ones.
Our Process
Set it and forget it. We monitor 48 hours.
The rest happens in the background — no agents on every machine, no network interruptions, no production impact.

Pick a time that works. We'll confirm your booking and send you a calendar invite.
Time: 2 minutes

We scope your environment, confirm asset inventory, and walk through the setup.
Time: 15–30 minutes

Your team installs one agent, adds a DNS record, and approves read-only M365 access.
Time: 30 minutes of your time

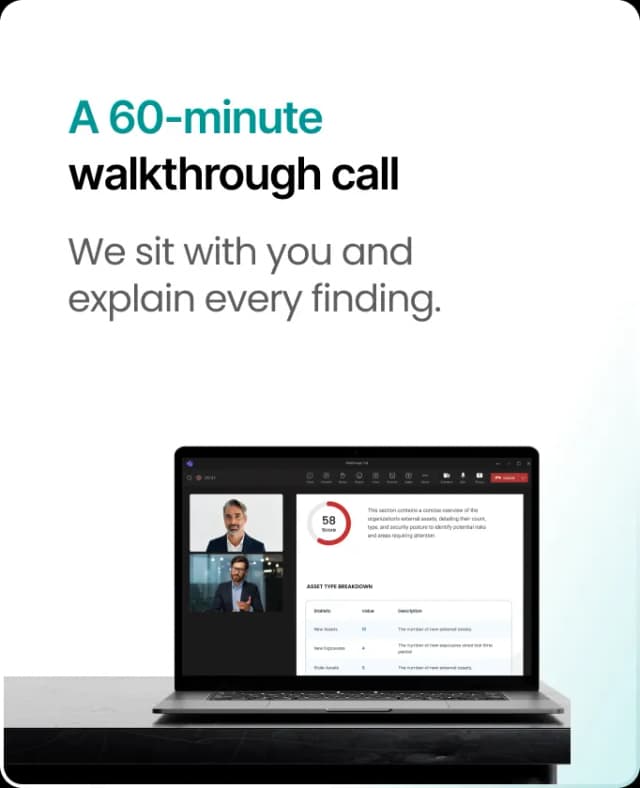
We deliver your 25+ pages report and spend 45–60 minutes unwrapping it.
Time: 45–60 minutes of your time

See it in action.
Download a sample report.
Less than 30 minutes of your team’s time.
A complete security baseline in 3 days.
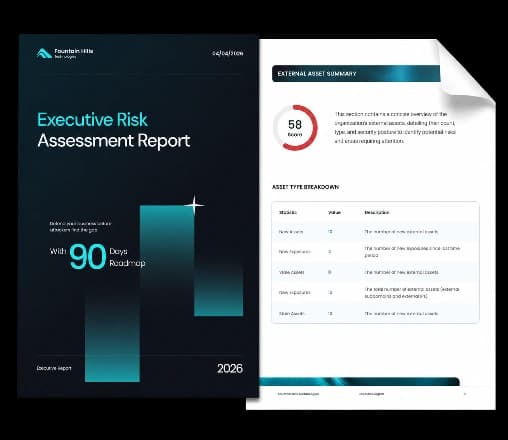

See it in action.
Download a sample report.
Less than 30 minutes of your team’s time.
A complete security baseline in 3 days.

Get the Sample Report

Sounds Familiar?
Sounds Familiar?This Security Jumpstart Is For You If...
This Security Jumpstart Is For You If...
You just closed an acquisition
You're inheriting infrastructure you haven’t mapped yet. Post-acquisition due diligence shouldn’t be optional.
You're 90 days into a new IT role
First 90 days. You need to know what you're walking into before you own the risk.
Cyber insurance renewal coming up
The insurer is asking questions you can’t fully answer yet. Get ahead of the audit.
Something felt off recently
Nothing confirmed — but now your CEO is asking ‘how exposed are we?’ and you need answers fast.
You grew faster than your security did
Nothing confirmed — but now your CEO is asking ‘how exposed are we?’ and you need answers fast.
You know this is simply overdue
A quiet, persistent awareness that you're running production on infrastructure you haven’t truly looked at.
You just closed an acquisition
You're inheriting infrastructure you haven’t mapped yet. Post-acquisition due diligence shouldn’t be optional.
You're 90 days into a new IT role
First 90 days. You need to know what you're walking into before you own the risk.
Cyber insurance renewal coming up
The insurer is asking questions you can’t fully answer yet. Get ahead of the audit.
Something felt off recently
Nothing confirmed — but now your CEO is asking ‘how exposed are we?’ and you need answers fast.
You grew faster than your security did
Nothing confirmed — but now your CEO is asking ‘how exposed are we?’ and you need answers fast.
You know this is simply overdue
A quiet, persistent awareness that you're running production on infrastructure you haven’t truly looked at.

True Story :
The Acquisition Case Study
It started with a casual email.
A manufacturer acquired a small company.
One quick scan uncovered critical risks no one knew existed.
11
Breached
3
Critical
151
High Severity
48/100
M365 Score
After that casual email, they had a board-ready report, a scored security baseline across all four surfaces, and a 90-day remediation roadmap
Their team started patching the PowerAlert device that afternoon.
It started with a casual email.
A mid-market manufacturer in the Midwest had just acquired a small operation in Ohio. Standard deal. The integration was underway — HR, payroll, insurance, all the usual checklists, somewhere near the bottom of that list was IT. The scan took 30 minutes to setup.
The Turn
What they uncovered in the next 72 hours —
they weren't even asking the right questions.
11
Breached
Employee credentials found on the dark web
3
Critical
Vulnerabilities — full system compromise risk
151
High Severity
Issues requiring action within 30 days
48/100
M365 Score
Microsoft security baseline — failing
127
Exposures on one device
A single powerAlert unit — a battery backup controller — had 127 individual security exposures, all rated critical. It had been on the network for years, nobody knew.
7
Accounts with no MFA
Seven user accounts had no multi-factor authentication. Forty more had passwords unchanged in over a year. Four inactive accounts were still open and accessible.
3 days later
After that casual email, they had a board-ready report, a scored security baseline across all four surfaces, and a 90-day remediation roadmap.
Their team started patching the PowerAlert device that afternoon.
Not ready to talk to us?
That's fine. Start here.
Use this self-assessment checklist to identify gaps, benchmark your current security posture, and understand where your biggest operational risks may exist — before you commit to a conversation.
Just a clear, honest picture of where the gaps might be — on your terms.

Built for manufacturing
Focused on real OT/IT security challenges — not generic enterprise IT checklists.
Practical, operations-focused insights
Identify gaps that impact uptime, recovery, and operational resilience.
Six security dimensions scored
Network Architecture, Access Controls, Backup & Recovery, Vulnerability Management, Monitoring & Detection, and People & Process.
Complete in 15 minutes
Get an instant readiness score you can share with leadership and use to prioritize next steps.
Complete in 15 minutes
Get an instant readiness score you can share with leadership and use to prioritize next steps.
Built for manufacturing
Focused on real OT/IT security challenges — not generic enterprise IT checklists.
Practical, operations-focused insights
Identify gaps that impact uptime, recovery, and operational resilience.
Six security dimensions scored
Network Architecture, Access Controls, Backup & Recovery, Vulnerability Management, Monitoring & Detection, and People & Process.
Complete in 15 minutes
Get an instant readiness score you can share with leadership and use to prioritize next steps.
Built for manufacturing
Focused on real OT/IT security challenges — not generic enterprise IT checklists.
Just a clear, honest picture of where the gaps might be — on your terms.